Our Consulting & Independent Third-Party Audits Solution
For businesses needing specialized expertise
Get the guidance and independent audit support your business needs.
Whether you need help understanding a regulation or preparing for an independent audit, URS can connect you with the appropriate expertise.
Cybersecurity Compliance Consulting
Hourly or project-based consulting for requirements such as:
CMMC
NIST
PCI DSS
Other applicable cybersecurity regulations and frameworks.
Get focused guidance based on your organization's compliance needs.
Independent Third-Party Audits
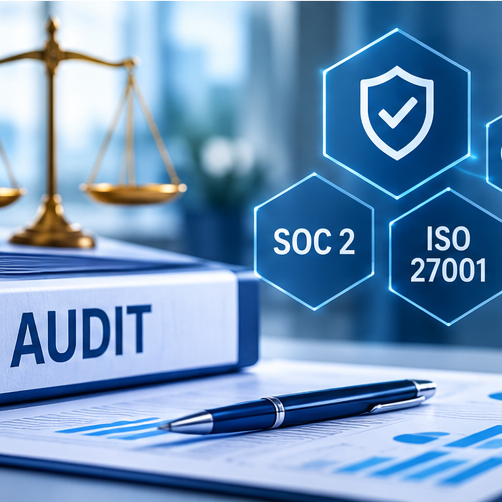
Through our strategic audit partner, businesses can access independent audit services for:
CMMC
SOC 2
ISO 27001
HITRUST
Other applicable frameworks.
Our audit partner's experience includes:

Additional credentials include SOC 2, FedRAMP, and CMMC C3PAO experience, as stated in the partner's service information.
Why it matters: Many regulatory frameworks require independent, third-party assessment of their cybersecurity compliance. While self-assessments can serve as periodic internal checkpoints, they cannot replace the depth, expertise, and objectivity that quality third-party evaluations offer.
Designed to work alongside your existing MSP for implementation, monitoring, and ongoing maintenance.